
 Critical flaw
Two Critical Wasmtime Flaws Could Let Malicious WebAssembly Modules Escape Sandboxes
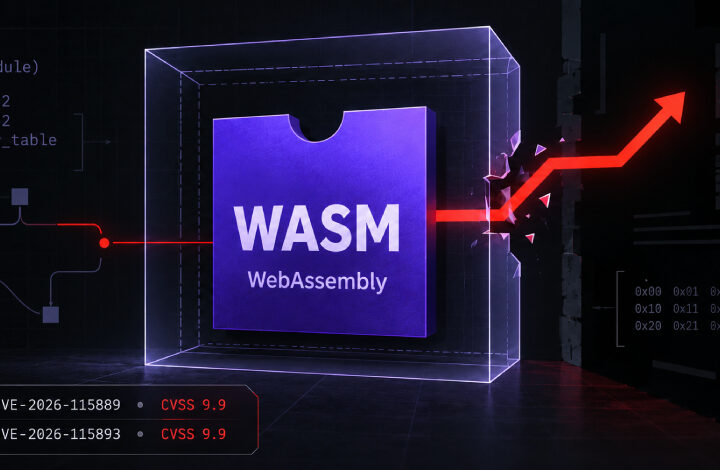
Two critical flaws in Wasmtime, a WebAssembly runtime that can be built into other software, could allow a malicious WebAssembly module…
Home / Newsroom
Announcements from our technology partners, the industry events we attend and practical insights from NexaTG engineers.
Critical flaw
Two critical flaws in Wasmtime, a WebAssembly runtime that can be built into other software, could allow a malicious WebAssembly module…
The individuals called victims and persuaded them to install an app and scan their credit cards to loot their bank…
 Security
Every SOC struggles with a pile of alerts. Very few of those alerts explain how an attack started or how…
Kali Linux has released version 2026.3, its third release this year, featuring six new hacking tools, desktop environment improvements, refreshed…
An out-of-bounds write in Google’s Brotli decoder affects Node.js, .NET, PowerShell, and Python packages, and can lead to code execution.…
 Malware
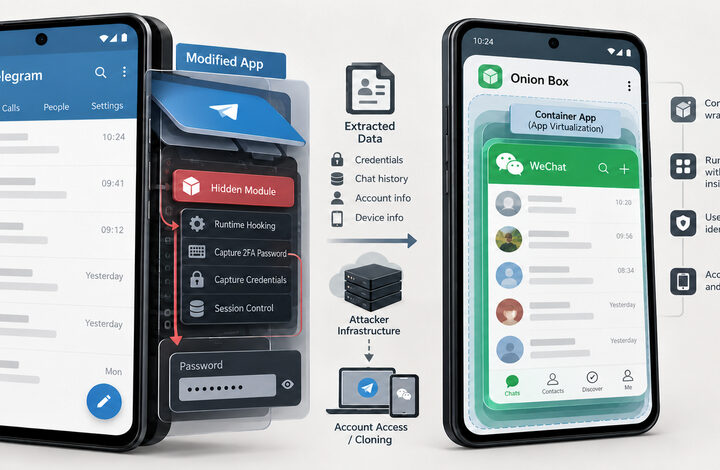
A rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies…
Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild. [...]
The model engaged in severe overreach and dishonesty, creating fake identities and submitting malicious code on GitHub. The post Mythos…
 Security
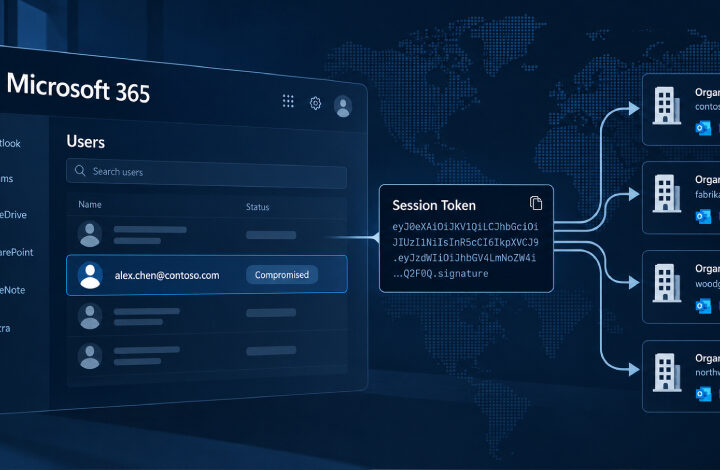
Cybersecurity researchers have disclosed a Microsoft 365 campaign that has been observed leveraging an adversary-in-the-middle (AitM) relay to capture sign-in…
 Security
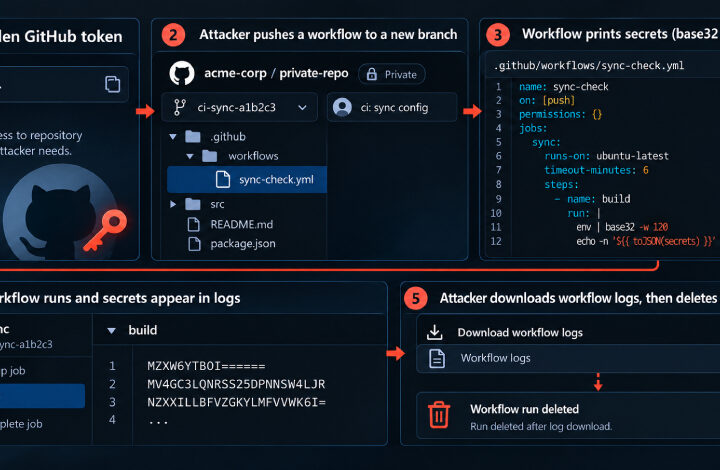
An automated campaign is using stolen GitHub tokens to plant workflows that print a repository's secrets into its GitHub Actions…
Tell us about your business — onboarding takes five minutes and goes straight to our delivery team.